
Cybersecurity / MSSP Operations Platform
WeWatch Desk
A multi-tenant SOC case desk for MSSP alert triage and customer communication
Overview
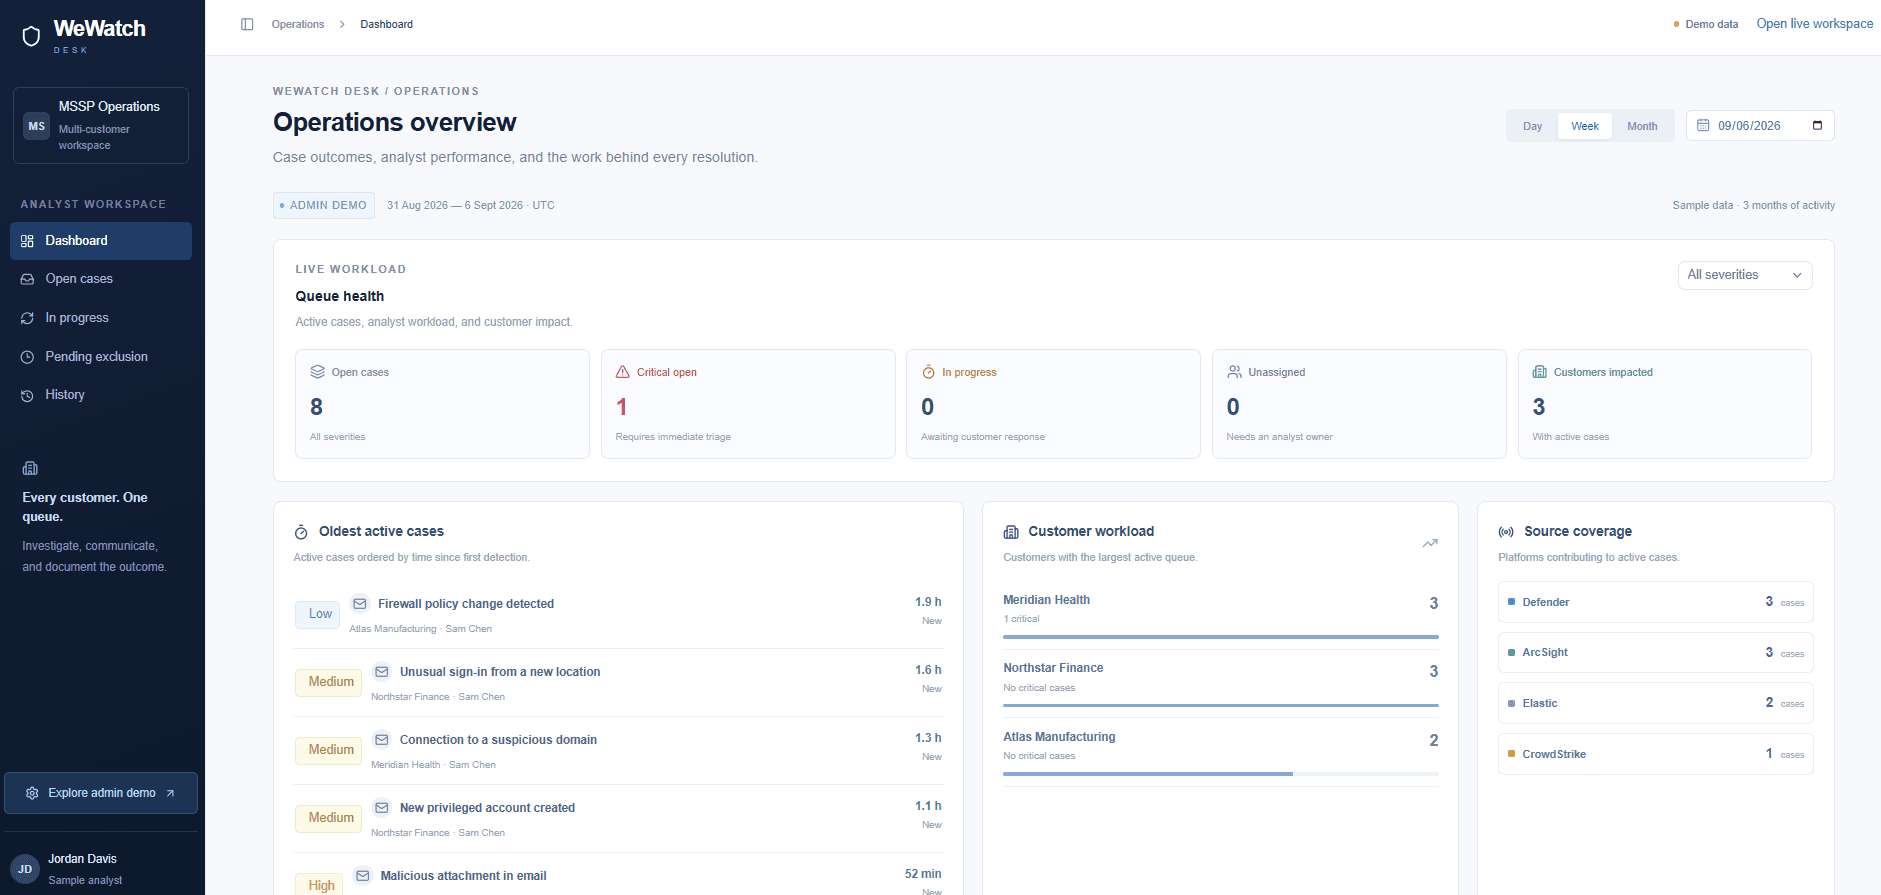
A multi-tenant SOC case management desk for an MSSP-style workflow: alerts from multiple security platforms are correlated into a single queue per analyst, with SLA tracking, MITRE ATT&CK context, and built-in customer communication.
The Problem
MSSP analysts juggling alerts across a customer's CrowdStrike, Elastic, Microsoft Defender and ArcSight deployments end up working from disconnected consoles, with no shared view of SLA status across customers and no consistent way to keep each customer informed as a case progresses.
The Approach
WeWatch Desk pulls alerts from each connected platform into one case queue, automatically combining matching alerts into a single case while keeping the original per-platform detail available underneath. Each case carries SLA timing, MITRE ATT&CK mapping, an evidence and occurrence timeline, and a built-in customer-email workflow, with a separate admin command center tracking resolution outcomes and analyst performance across every customer.
Where It Stands
Currently built and running against sample data (demo customers, three months of generated activity) to validate the workflow end-to-end; not yet connected to live alert feeds or handling real customer traffic.
Architecture
- Unified case queue that combines alerts from multiple sources, keeping per-platform detail inside each case
- SLA tracking with overdue indicators, severity and status filtering across the queue
- Case detail view with MITRE ATT&CK mapping, evidence and occurrence timeline, raw JSON and similar-case matching
- Built-in customer communication: templated incident emails with a live branded preview before sending
- Admin command center: resolution-outcome analytics (true positive / false positive / benign), analyst performance leaderboard, audit log
- Multi-tenant customer and user management with per-customer notification contacts
- Source coverage across Microsoft Defender, ArcSight, Elastic and CrowdStrike
Key Features
Screenshots
Technologies
Status
In Development